A Profiling Opt-Out Is Useless If the Ranker Never Gets It
A preference-center toggle can change a database row while recommendation and audience models keep scoring the person. The control needs an enforceable path through every downstream system.
October 7, 2026 · 7 min read
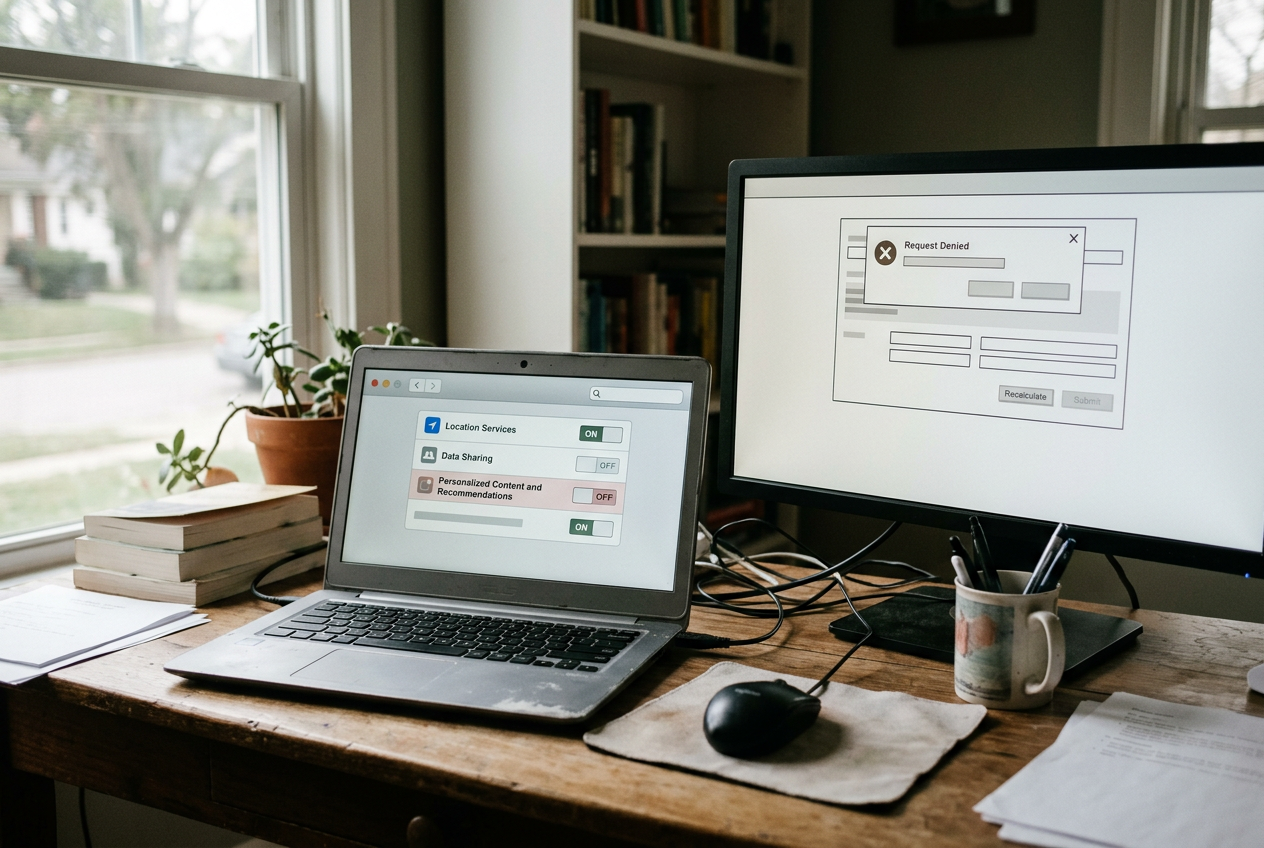
Take an ordinary retail website with a blue preference-center toggle labeled “Personalized offers.” A customer switches it off, sees a confirmation banner and assumes the matter is settled. The consent service records the change correctly. Hours later, the site’s recommendation model still places high-margin products at the top, while an audience platform includes the same customer in a campaign built from predicted purchase intent.
Nothing necessarily failed at the interface. The failure sits in the integration path between that blue toggle and the models that use behavior to rank people, products or messages.
This distinction matters because an opt-out is a policy decision expressed through software. If the policy applies to profiling, the engineering requirement cannot stop at “store the preference.” It must identify the relevant processing purpose, distribute the decision to systems acting for that purpose, block incompatible processing and produce evidence that the block worked.
The requirement is about processing, not interface state
Under the European Union’s General Data Protection Regulation, Article 21(2) says: “Where personal data are processed for direct marketing purposes, the data subject shall have the right to object at any time to processing of personal data concerning him or her for such marketing, which includes profiling to the extent that it is related to such direct marketing.” Article 21(3) then states that the data “shall no longer be processed for such purposes.”
That is an enforceable requirement within the GDPR’s scope, not a proposed design principle. It also is not a universal rule for every model use. Whether a recommendation system falls within direct marketing, and which legal basis or exception applies, depends on facts and jurisdiction. This analysis is not legal advice.
US state privacy laws use different categories. California’s regime covers opt-outs from sale or sharing and requires covered businesses to process applicable opt-out preference signals, such as the Global Privacy Control, under its regulations. Colorado gives consumers rights to opt out of targeted advertising and certain profiling tied to decisions with legal or similarly significant effects. Those rights are not interchangeable, and a generic “privacy opted out” field loses distinctions the downstream system may need to enforce.
The blue toggle therefore needs more than a Boolean value. A useful record identifies the person or device the choice covers, the disallowed purpose, the source of the request, its effective time and the policy version used to interpret it. Otherwise, one team may read “false” as no marketing email while another reads it as no personalized ranking.
Follow the toggle past the consent database
The first write usually lands in a consent or preference store. From there, many architectures publish an event to a message bus, which is software that distributes the same update to multiple systems. The event may update a customer profile, an identity service and the marketing platform. The recommendation stack often sits elsewhere.
That stack may read behavioral features from a feature store, a database that supplies model inputs consistently during training and live prediction. Recent clicks, product categories and predicted spending propensity become inputs to a ranker. The ranker assigns scores, then returns an ordered set of products. An audience-selection job may reuse the propensity score later to decide who receives an offer.
At each handoff, the opt-out can disappear.
A common failure starts with identity. The preference center records the customer account ID, but the recommendation service requests predictions under a browser cookie or mobile advertising identifier. Unless an identity service links those identifiers and propagates the restriction, the model sees an apparently eligible device. Logging out can make the problem worse if anonymous personalization continues under a cookie that the account-level preference never reached.
Timing creates another gap. A consent service may publish updates within seconds while a recommendation service imports eligibility records in a nightly batch. During that interval, the website truthfully displays the saved choice, yet the ranker operates from yesterday’s state. The company has created a defined period of continued processing, whether anyone documented it or not.
The blue toggle can also reach campaign delivery without reaching scoring. A suppression list prevents an ad platform from sending an offer, but an upstream model still calculates purchase intent and places the person into a high-value segment. If the applicable instruction prohibits profiling for that purpose, suppressing the final message is too late. The prohibited computation already occurred.
Put the control before the model call
The strongest design checks purpose-specific eligibility before assembling features or requesting a score. A policy-enforcement service receives the subject identifier, intended purpose and requested operation, then returns allow, deny or an explicit error. A deny response stops the model call. An error should normally fail closed for the restricted purpose rather than quietly treating an unavailable preference service as permission.
A live network check adds latency and creates a new dependency. Teams can reduce that cost by distributing signed or versioned restriction records to a local cache near the ranking service, but cached decisions need a short, documented freshness target and a reliable invalidation path. A cache that refreshes once per day merely disguises batch delay as an optimization.
Candidate filtering after scoring is cheaper to retrofit, and it may be enough when the rule concerns only delivery or display. It does not prove that profiling stopped. Engineers and policy owners need to decide which operation the restriction covers: feature retrieval, inference, segment assignment, activation or some combination. The answer belongs in machine-readable policy and system tests, not only in a privacy notice.
Historical data requires a separate decision. An objection to profiling for direct marketing does not automatically describe every retention, deletion or model-training obligation. Removing a person from future scoring can happen immediately without retraining the model. Removing their past records from training data is a different control, and reversing their influence on an already trained model may require retraining or a validated unlearning method.
That distinction should appear in the interface. A preference center must not imply that switching off personalized offers erased stored history if the implemented action only blocks future marketing inference. Precise wording creates less legal and engineering debt than a broad promise that no system can verify.
Receipts have to connect the request to the decision
An audit trail should start with the blue toggle’s receipt: subject key, purpose, requested state, effective time and policy version. Downstream logs then need to show that each relevant service received the change and enforced it. A delivery-platform suppression record alone cannot demonstrate that the recommendation model stopped scoring.
For a live ranker, useful evidence includes the policy decision attached to the request, whether feature retrieval occurred, whether inference ran and which policy version governed the outcome. Logs should avoid copying raw behavioral features unless investigators need them; proving that a gate denied a call does not require creating another store of sensitive data.
Periodic reconciliation catches silent drift. The consent store’s restricted population can be compared with eligibility indexes, recent inference logs and exported audience membership. These checks cost storage and engineering time, while strict pre-inference gates can reduce the amount of personalized inventory available to a campaign. That is the tradeoff created by the policy choice.
Continuing to score people because enforcement would lower campaign reach is not a technical fallback.
Tests need to cross system boundaries. A synthetic account can switch off the blue toggle, browse products and then trigger the same APIs used by the site, campaign builder and audience exporter. The expected result is not merely a changed settings response. The test should show no prohibited feature fetch, no prohibited inference and no new audience membership after the documented propagation window.
Deletion jobs, vendor outages and identifier changes deserve failure tests too. If the policy service is unavailable, the recommendation layer should have a defined response. If an account merges with another identity, the more restrictive preference may need to prevail until the conflict is resolved. If a vendor cannot accept purpose-specific restrictions, sending that vendor the data is an architectural choice, not an unavoidable property of machine learning.
A team evaluating its own blue toggle can begin with one trace: save the opt-out, capture its event identifier and follow it until the next recommendation request and audience build. Any system that cannot show how it received or enforced the instruction is outside the control plane, even if its owner says the preference is “honored.”
Questions people ask
Does turning off personalized ads require deleting my data?
Not necessarily. An opt-out may require a company to stop specified processing or sharing without erasing every retained record. Deletion rights and retention duties are separate questions. The interface should state whether it blocks future scoring, removes audience membership, changes data sharing or also starts a deletion workflow.
Can a company suppress ads but keep calculating my profile?
Technically, yes. A delivery system can exclude someone after an upstream model has calculated a score. Whether that meets the applicable requirement depends on what the opt-out covers. If profiling for the relevant purpose must stop, the control needs to block feature retrieval or inference before the score is produced.
How quickly should an opt-out reach recommendation systems?
The required timing depends on the governing rule and the company’s stated policy, but the engineering target should be explicit and tested. A site should not imply immediate effect while downstream systems refresh overnight. Synchronous checks offer fresher enforcement; replicated local restrictions reduce latency but introduce a measurable propagation window.
What is the simplest audit test for a profiling opt-out?
Create a controlled account, record the opt-out receipt and trigger the same recommendation and audience workflows used in production. Then verify that restricted model calls did not run and that no new segment membership appeared. A changed preference row or confirmation banner is evidence of intake, not downstream enforcement.
One story a day
The story of the day, in your inbox
One real story about AI each morning — no hype, no alarm, just company for the road.